The world of cybersecurity has just been handed a wake-up call that’s both terrifying and illuminating. Picture this: a single line of malicious code, hidden in plain sight within an open-source tool, quietly siphoning secrets from thousands of corporate systems. This isn’t just a breach—it’s a masterclass in how digital ecosystems are now battlegrounds for invisible wars. And the weapon? A poisoned vulnerability scanner called Trivy, which became the Trojan horse for a far more insidious attack on LiteLLM, an AI proxy gateway used by giants like Amazon, Cisco, and Samsung. Let me tell you, this isn’t just about hacked servers. It’s about the fragility of trust in the digital age.
What makes this particularly fascinating is how the attack unfolded. TeamPCP, the shadowy group behind this, didn’t storm the gates—they slipped in through the back door. They compromised Trivy, a tool designed to catch vulnerabilities, and used it to plant a backdoor in LiteLLM’s CI/CD pipeline. That’s like giving a burglar the keys to your vault under the guise of a locksmith. The irony here is almost poetic. The very tools meant to protect us became the instruments of our undoing. And this wasn’t a one-off; it was a meticulously orchestrated three-stage payload that exfiltrated secrets as soon as a Python interpreter booted up. Imagine your company’s most sensitive data—API keys, cloud credentials, Kubernetes configs—being harvested without ever being explicitly imported. That’s the horror of it: the attack is silent, invisible, and utterly relentless.
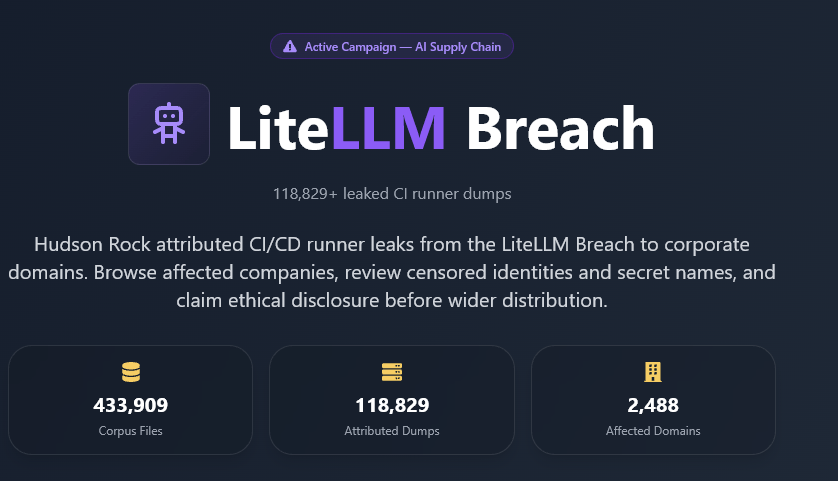
Now, let’s talk about the 153GB data dump that Hudson Rock uncovered. This isn’t just a pile of files—it’s a digital time capsule of corporate negligence. The sheer scale of it is staggering: 433,909 files, 118,829 CI runner dumps, and 2,500 companies potentially exposed. But here’s the kicker: many of these files have no clear attribution. No company email, no custom domain, no internal server name. It’s like finding a treasure chest with no map. Organizations are left wondering, 'Was it us?' while their secrets sit in the dark, waiting to be weaponized. This raises a deeper question: How many companies are unknowingly hosting their own digital skeletons in this database? What many people don’t realize is that the real threat here isn’t just the breach itself—it’s the existential crisis it creates for corporate security teams who now have to audit every single CI/CD pipeline like it’s a ticking bomb.
Take a look at the list of victims: AWS, Salesforce, Siemens, John Deere. These aren’t just names—they’re pillars of modern infrastructure. The fact that such foundational systems were compromised through a seemingly innocuous open-source tool is a chilling reminder of how interconnected our digital lives have become. But here’s what’s even more alarming: the attack didn’t rely on zero-day exploits or brute force. It exploited the very trust we place in open-source ecosystems. And that’s where the real vulnerability lies. In my opinion, the open-source model is a double-edged sword. It fosters innovation but also creates a monoculture of trust that attackers can exploit. The idea that a single compromised tool can ripple through thousands of organizations is a wake-up call for developers and security teams alike.
The attribution challenge is another layer of this nightmare. Even when you find a file with a committer email from SiriusXM, the real story is buried in infrastructure endpoints like gitlab.adswizz.com. This isn’t just about technical sleuthing—it’s about the breakdown of accountability in a world where infrastructure is decentralized and anonymized. A detail that I find especially interesting is how the breach exposed the fragility of our current SOC (Security Operations Center) frameworks. If your alert system can’t distinguish between a real threat and a red herring, then what’s the point of having one at all? This isn’t just a technical failure; it’s a systemic one. It forces us to confront the uncomfortable truth that our defenses are as good as the data we feed them.
And let’s not forget the ethical implications. Hudson Rock’s decision to provide a free lookup tool is commendable, but it also highlights a disturbing trend: the normalization of corporate data exposure. If this level of compromise is now routine, how do we even begin to measure the true cost of such breaches? The psychological impact on developers and security professionals is profound. You’re no longer just defending against external threats—you’re constantly questioning the integrity of the tools you rely on daily. What this really suggests is that the next frontier in cybersecurity isn’t just about better firewalls or AI-driven threat detection. It’s about rebuilding trust in the very systems that underpin our digital world.
Looking ahead, this breach is a harbinger of things to come. As AI becomes more deeply integrated into our workflows, the attack surface will only expand. The LiteLLM hack isn’t an outlier—it’s a blueprint for future attacks. And yet, there’s a silver lining. This crisis might finally push organizations to rethink their approach to open-source security. Maybe it’s time to stop treating CI/CD pipelines as sacred cows and start treating them with the scrutiny they deserve. Because if there’s one thing this breach teaches us, it’s that in the digital age, trust is a liability—and the cost of getting it wrong is nothing less than the collapse of our global infrastructure.